 Live Chat
 Log In
Cloudflare Blocks Explained for Developers
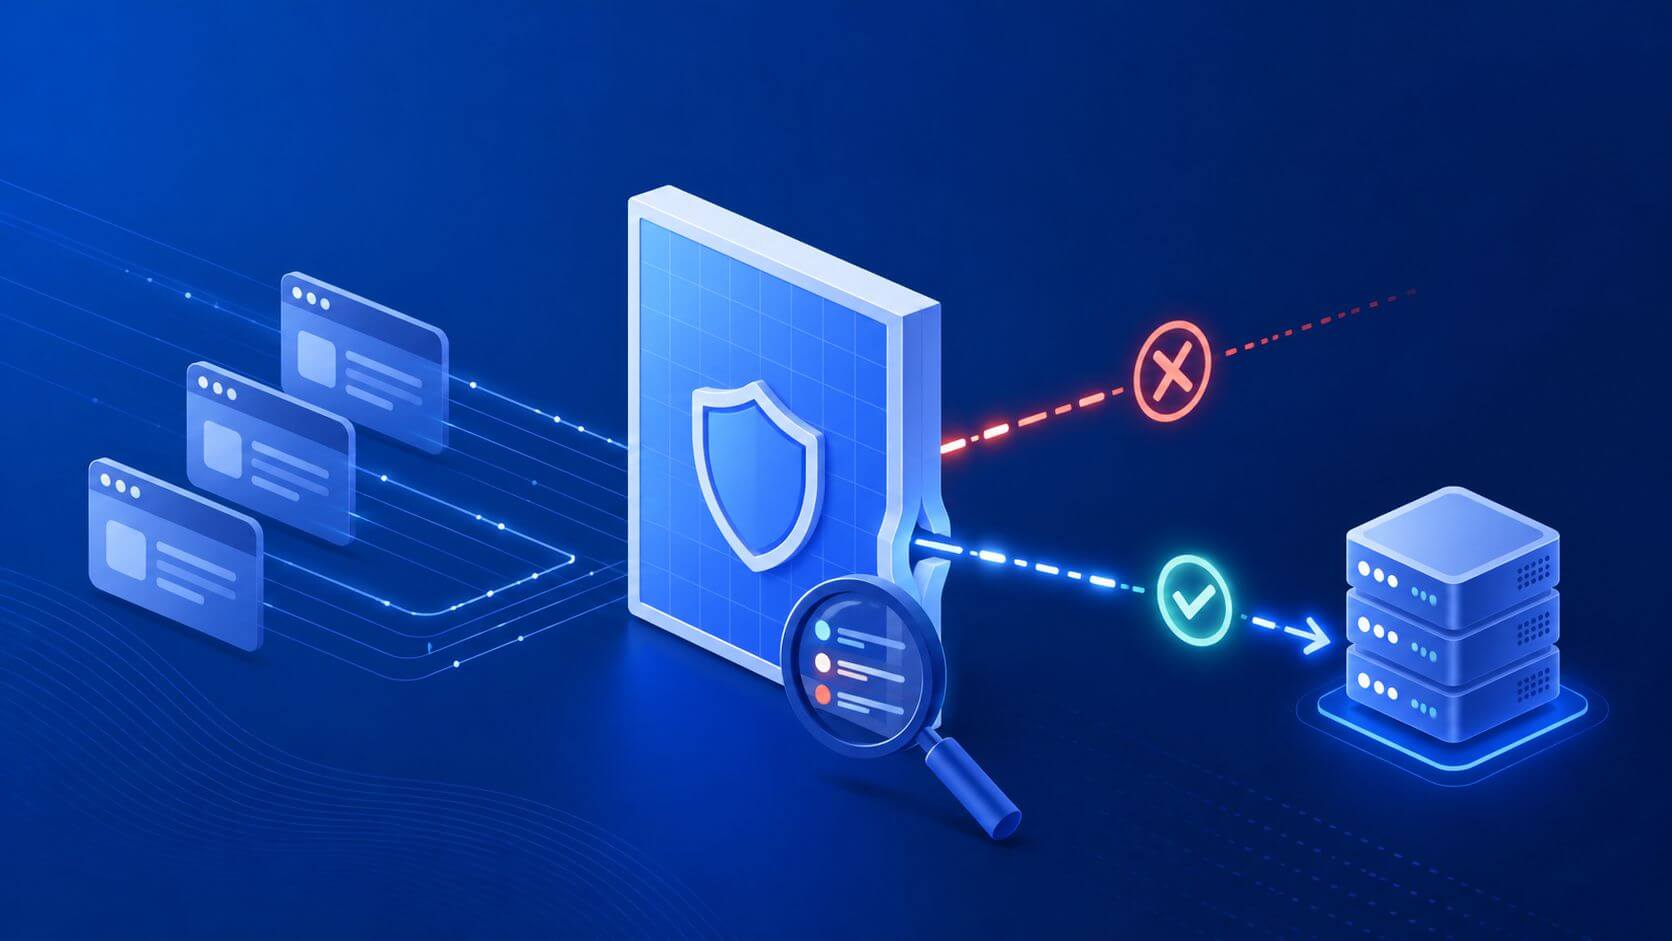
Cloudflare blocks can break scraping, monitoring, QA, and automation workflows quickly. A request that worked yesterday may suddenly return a 403, 1020-style access denied response, 1015 rate limit, JavaScript challenge, CAPTCHA, or an interstitial page instead of the expected content.
For developers, the important question is not just “How do I get past this?” The better question is: Why did this request become risky, and what should change in the workflow?
Cloudflare blocks usually happen when traffic triggers rules from the Web Application Firewall, Bot Management, rate limiting, geo policies, or custom security settings configured by the site owner. The signals may include IP reputation, ASN, request rate, TLS behavior, browser fingerprint, headers, cookies, geo mismatch, or suspicious navigation patterns.
If you are using web scraping proxies, browser automation, SEO monitoring, price tracking, or uptime checks, the goal should be to reduce unnecessary friction responsibly. That means validating access permissions, shaping traffic carefully, using the right proxy route, respecting site rules, and measuring block rate and cost per successful request before scaling.
What Are Cloudflare Blocks?
Cloudflare blocks are security responses applied before a request reaches the origin server. Cloudflare sits between the visitor and the website. When a request looks risky, violates a rule, exceeds a limit, or comes from a restricted location or network, Cloudflare may block, challenge, throttle, or redirect the request.
Developers may see Cloudflare blocks as:
- 403 Forbidden
- 1020-style access denied messages
- 1015 rate limit responses
- JavaScript challenge pages
- CAPTCHA or Turnstile challenges
- interstitial browser checks
- connection resets
- repeated redirects
- soft blocks that return content but not the expected page
A Cloudflare block does not always mean the IP is bad. It can also mean the request pattern, headers, browser environment, session state, or path behavior triggered a rule.
Why Cloudflare Blocks Matter
Cloudflare blocks create real operational cost.
They can cause:
- missing price data
- failed SEO rank checks
- broken ad verification workflows
- incomplete product monitoring
- delayed dashboards
- higher retry volume
- wasted proxy spend
- increased infrastructure cost
- lower trust in reports
- noisy engineering alerts
Blind retries usually make the problem worse. If the same risky request is repeated at higher volume, block rates may increase and cost per successful request can rise sharply.
A better approach is to classify the block, reduce the risky signal, and measure whether valid output improves.
Common Cloudflare Block Types
| Block Type | What It Usually Means | Better First Response | | 403 Forbidden | Request denied by rule, bot score, geo policy, or access control | Inspect response body, route, headers, and session state | | 1020-style access denied | WAF or custom security rule denied the request | Confirm access permission and reduce rule-triggering behavior | | 1015 rate limited | Too many requests within a defined window | Slow down, add jitter, use backoff, and avoid retry storms | | Browser challenge | Cloudflare wants browser proof or JavaScript execution | Use browser only when access is permitted and rendering is required | | CAPTCHA / Turnstile | Higher-risk request needs human or interaction proof | Reassess workflow, reduce friction triggers, and avoid pushing harder | | Soft block | Page loads but expected content is missing or changed | Validate content structure before counting success | | Connection reset | Edge, route, or policy closed the connection | Reduce concurrency and compare routes |
The same status code can have different causes. A 403 on one path may be caused by a custom rule, while a 403 on another may come from bot scoring or geo policy.
How Cloudflare Evaluates Requests
Cloudflare can evaluate multiple layers of a request before deciding whether to allow, challenge, throttle, or block it.
Common signal groups include:
- IP reputation
- ASN and network type
- country, region, or city
- request path and query parameters
- WAF rule matches
- request rate
- TLS and HTTP behavior
- header consistency
- browser fingerprint
- cookies and session state
- JavaScript execution
- bot score
- historical behavior
- custom rules configured by the site owner
This means the fix is rarely one setting. Changing the proxy IP may help if the problem is network reputation. But it will not fix aggressive concurrency, inconsistent headers, missing cookies, or a browser fingerprint mismatch.
For broader context on detection layers, see How Websites Detect Proxy Traffic.
Cloudflare WAF Blocks
The Web Application Firewall can block requests based on rules. These rules may target suspicious paths, query parameters, payloads, user agents, countries, IP ranges, or patterns associated with abuse.
Examples of WAF-triggering behavior include:
- unusual query parameters
- repeated requests to sensitive paths
- malformed headers
- suspicious payloads
- high-risk URL patterns
- restricted countries or ASNs
- direct access to paths that expect prior navigation
If a WAF rule blocks the request, retrying the same request from many proxies may not help. The request itself may be the problem.
Better responses include:
- confirm the path is allowed
- remove malformed or unnecessary parameters
- follow normal navigation flow
- avoid restricted routes
- use official APIs or feeds where available
- request permission or allowlisting if you have a legitimate business relationship
Cloudflare Rate Limiting
Rate limits are one of the most common reasons developers see Cloudflare blocks.
A 1015 or similar rate-limit response means the request volume exceeded a threshold. The threshold may apply by IP, path, account, country, ASN, cookie, or behavior pattern.
Common rate-limit triggers include:
- too many requests per second
- synchronized cron jobs
- repeated retries after errors
- high concurrency on one path
- crawling sensitive pages too quickly
- many similar requests from one subnet
- no caching or conditional requests
How to Reduce Rate-Limit Blocks
Use smoother traffic patterns:
- add per-domain concurrency limits
- spread jobs across longer windows
- add random jitter
- use exponential backoff
- cache stable pages
- use conditional requests where appropriate
- avoid retry storms
- reduce volume on sensitive paths
A slower, steady workflow often produces more valid data than a faster workflow that triggers blocks and retries.
Cloudflare Bot Management Signals
Cloudflare Bot Management may evaluate whether a request looks automated based on many signals.
These may include:
- IP reputation
- TLS fingerprint
- HTTP headers
- browser behavior
- JavaScript execution
- cookie state
- request timing
- navigation path
- known automation signatures
If a request claims to be a browser but does not behave like one, risk can increase.
For example:
- Chrome User-Agent with non-Chrome TLS behavior
- browser profile from one country with proxy IP from another
- no cookies across repeated page visits
- direct access to deep endpoints without prior navigation
- identical timing across thousands of requests
- missing expected browser headers
For browser-side issues, review Browser Fingerprinting for Web Scraping.
Proxy Type and Cloudflare Blocks
Proxy type can influence Cloudflare outcomes, but it is not the only factor.
Datacenter proxies are fast and cost-effective for low-friction public pages, APIs, sitemaps, and workloads where hosting ASNs are accepted.
Residential proxies may perform better on consumer-facing pages, local content, regional checks, and workflows where residential ISP routing reduces network-level suspicion.
ISP proxies can help when stable sessions and stronger reputation than standard datacenter routes matter.
The right route depends on workload sensitivity.
For a deeper comparison, see Datacenter vs Residential vs ISP Proxies Explained.
Rotating vs Sticky Sessions
Cloudflare blocks can increase when sessions are unstable.
Rotating IPs on every request may work for stateless public pages, but it can break workflows that need cookies, pagination, storefront selection, cart state, or JavaScript tokens.
Use rotating sessions for:
- stateless public pages
- broad URL collection
- independent SERP checks
- low-risk discovery crawls
Use sticky sessions for:
- pagination
- local SEO batches
- regional storefront checks
- account workflows
- cart-like flows
- browser automation
- multi-step page journeys
If the browser identity stays the same but the IP changes repeatedly, the session may look inconsistent.
For more, see Rotating vs Static Proxies.
Geo and Locale Consistency
Cloudflare rules can include country, region, or ASN policies. Even when the site owner does not explicitly block a country, geo mismatch can still increase risk.
Geo mismatch happens when:
- proxy country conflicts with browser timezone
- Accept-Language does not match region
- currency or storefront selection conflicts with IP location
- cookies suggest one country while IP suggests another
- session moves between countries mid-flow
For SEO, e-commerce, travel, and ad verification, this is also a data quality issue. A page that loads from the wrong region may not be useful.
Validate:
- proxy country or city
- returned currency
- page language
- local content
- storefront region
- shipping location
- timezone
- cookies and session state
WebRTC, DNS, and Browser Leaks
Browser automation can trigger additional risk if network signals leak around the proxy.
Potential issues include:
- WebRTC exposing local or alternate network details
- DNS resolving from a different region
- timezone mismatch
- browser profile mismatch
- proxy bypass rules
- inconsistent geolocation permissions
If HTTP traffic exits through one route but browser-side signals suggest another, the session becomes less coherent.
For deeper troubleshooting, see WebRTC Leaks: Why They Break Anti-Detect Setups.
How to Diagnose Cloudflare Blocks
Use a structured diagnostic process.
Step 1: Confirm Permission and Scope
Before technical troubleshooting, confirm that the workflow is allowed. Check terms, access rules, robots guidance where applicable, internal policy, and whether an official API or data feed exists.
Do not push through blocks on restricted, sensitive, authenticated, or prohibited routes.
Step 2: Identify the Block Type
Record:
- status code
- response body
- response headers
- path
- proxy route
- country
- user agent
- retry count
- timestamp
- whether a challenge page appeared
- whether expected content was present
Look for Cloudflare indicators such as edge headers or challenge pages.
Step 3: Compare Routes
Test the same request through different routes:
- direct access where appropriate
- datacenter proxy
- residential proxy
- ISP proxy
- target country route
If only one proxy type fails, network reputation or ASN may be involved.
Step 4: Reduce Concurrency
Lower request rate and concurrency for a controlled test. If blocks drop, the issue is likely volume, burstiness, or retries.
Step 5: Inspect Headers and Browser Behavior
Check whether the client profile is coherent:
- User-Agent
- Accept-Language
- Accept-Encoding
- Referer
- cookies
- TLS behavior
- browser fingerprint
- timezone
- WebRTC
- DNS
Step 6: Validate Content
Do not count a request as successful just because it returned HTTP 200. Confirm that required content exists.
What to Measure
Cloudflare troubleshooting should be measured with operational metrics.
| Metric | Why It Matters |
|---|---|
| Block rate | Shows how often requests hit Cloudflare denial or challenge responses |
| Success rate | Measures valid content returned |
| Soft block rate | Catches pages that load but lack expected content |
| Retry depth | Reveals hidden instability |
| CPSR | Measures cost per successful result |
| Session survival | Shows whether multi-step flows complete |
| Geo accuracy | Confirms location-sensitive validity |
| P95 latency | Detects route or edge pressure |
| Challenge rate | Tracks browser checks, CAPTCHA, or Turnstile prompts |
| Route performance | Compares proxy types and regions |
CPSR means cost per successful request.
In plain terms: CPSR tells you how much each valid result costs after proxy spend, compute, browser rendering, retries, and failed attempts.
Practical Ways to Reduce Cloudflare Blocks
Use these compliance-first practices:
- confirm the workflow is permitted
- prefer APIs or official data feeds where available
- reduce concurrency
- add jitter and backoff
- cache stable pages
- use conditional requests when appropriate
- align proxy region with target content
- use sticky sessions for multi-step flows
- avoid direct access to restricted paths
- keep headers coherent
- validate browser fingerprints
- detect soft blocks
- log failed responses for debugging
- monitor CPSR before scaling
For general troubleshooting, see Common Proxy Errors and How to Fix Them.
What Not to Do
Avoid these mistakes:
- retrying every block immediately
- rotating IPs aggressively mid-session
- treating CAPTCHA as something to force through
- using random header sets
- ignoring site terms or access restrictions
- scraping sensitive paths without approval
- using residential proxies everywhere without measuring CPSR
- counting HTTP 200 as success without content validation
- scaling before observing block rate and soft blocks
The safest and most reliable automation systems are measured, permission-aware, and designed around valid output.
Real-World Scenario: E-Commerce Price Monitoring
A price monitoring system checks product pages across several retailers. During a promotion week, Cloudflare challenge pages increase and price fields go missing.
The team investigates and finds three problems:
- all jobs run at the top of the hour
- retries happen immediately after failures
- regional storefront sessions rotate IPs too often
The improved setup:
- staggers crawl windows
- adds backoff after challenge responses
- uses residential proxies for regional product pages
- uses sticky sessions for storefront checks
- validates price, currency, and product title before storing data
The result is fewer soft blocks and better price coverage.
Real-World Scenario: Local SEO Monitoring
An SEO platform tracks local SERPs across many cities.
Some city checks return challenge pages, while others return wrong-location results. The team discovers that proxy location, language settings, and scheduling are inconsistent.
The improved setup:
- uses city-targeted residential routes
- aligns Accept-Language and search parameters
- reduces concurrency by city
- validates local pack addresses
- logs geo mismatch separately from hard blocks
Reports become more reliable because the system separates true ranking changes from collection issues.
Real-World Scenario: Travel Monitoring
A travel data workflow checks public fare landing pages.
The old setup hits dynamic endpoints directly without loading prior page state. Cloudflare challenges increase because the request flow does not match normal navigation.
The improved setup:
- follows the expected public page flow
- uses caching for stable pages
- limits checks to approved routes
- avoids sensitive checkout-like paths
- uses browser rendering only where required
The team reduces block rate without forcing high-risk automation.
Compliance and Governance
Cloudflare blocks often protect resources based on site owner rules. If a route is blocked, developers should consider whether automation is appropriate for that route.
A responsible process should include:
- approved domain list
- allowed path list
- blocked path list
- rate limits
- data minimization
- access review for authenticated content
- logging and audit trails
- escalation path for persistent blocks
- preference for official APIs where available
Persistent blocks should trigger review, not just more aggressive retries.
Developer Checklist
Before scaling a workflow behind Cloudflare:
- Confirm access permission.
- Identify the block type.
- Inspect response body and headers.
- Track block rate and soft block rate.
- Lower concurrency during diagnosis.
- Add backoff and jitter.
- Use caching and conditional requests.
- Align proxy region with target content.
- Use sticky sessions where continuity matters.
- Validate browser fingerprint consistency.
- Check DNS and WebRTC behavior for browser flows.
- Compare datacenter, residential, and ISP routes.
- Measure CPSR before scaling.
For implementation support, review SquidProxies proxy tutorials and broader proxy use cases.
Frequently Asked Questions
What are Cloudflare blocks?
Cloudflare blocks are denial, challenge, or rate-limit responses applied at the edge before a request reaches the origin server. They may appear as 403 responses, access denied pages, rate limits, or browser challenges.
What causes Cloudflare blocks?
Common causes include WAF rules, Bot Management scoring, rate limits, IP reputation, ASN policies, geo restrictions, suspicious headers, browser fingerprint issues, session mismatch, and aggressive request patterns.
What does Cloudflare 1015 mean?
A 1015-style response means the request was rate limited. Reduce concurrency, add backoff, stagger jobs, and avoid immediate retries.
What does Cloudflare 1020 mean?
A 1020-style access denied response usually means a firewall rule or custom security policy denied the request. Confirm the route is allowed and review request behavior, headers, geo, and path sensitivity.
Can proxies fix Cloudflare blocks?
Sometimes, if the issue is IP reputation, ASN, or geo. But proxies will not fix missing cookies, bad browser fingerprints, aggressive pacing, prohibited routes, or malformed requests.
Should I use residential proxies for Cloudflare-protected sites?
Residential proxies may reduce some network-level friction on consumer-facing pages, but they should be used responsibly and only where the workflow is permitted. Measure success rate, block rate, and CPSR before scaling.
Should I use a browser instead of HTTP requests?
Use a browser only when client-side rendering is required and access is permitted. For static or API-like pages, HTTP clients with caching and good pacing are often more efficient.
What metrics should I monitor?
Track block rate, success rate, soft block rate, retry depth, CPSR, session survival, geo accuracy, latency, challenge rate, and route performance.
How do I reduce Cloudflare blocks safely?
Reduce request rate, add jitter and backoff, use caching, align geo and headers, preserve sessions where needed, validate content, and use official APIs or permission-based access where available.
Final Thoughts
Cloudflare blocks are not random. They are responses to risk signals such as request rate, IP reputation, WAF rules, browser behavior, geo mismatch, or custom site policies.
The best developer response is structured diagnosis. Confirm access, classify the block, reduce risky signals, select the right route, validate returned content, and measure whether success rate and CPSR improve.
A reliable workflow does not depend on blind retries or constant proxy switching. It depends on coherent request design, responsible pacing, session stability, route selection, and clear metrics.
Related Articles
Understanding 403 Errors in Scraping: Causes, Fixes, and Metrics
Why scrapers encounter 403 Forbidden errors, how to quickly diagnose root causes, and the practical solutions that can reduce block rates and lower the cost per successful request.
Common Proxy Errors and How to Fix Them
A practical, operator-grade guide to diagnosing and fixing common proxy errors with clear decision paths, measurable signals, and production-ready tactics for marketing, eCommerce, travel, finance, and data teams.
How Websites Detect Proxy Traffic: Signals, Tests, and Practical Defenses
A practical guide to how websites detect proxy traffic, the signals they use, and how data teams can measure, design, and operate low-friction scraping and automation flows.